x
H H
Home / Products / Martinet

An Endpoint Agent
That Never Blinks

Martinet is an AI-native Endpoint Detection & Response (EDR), Extended Detection & Response (XDR) and Autonomous Security Operations platform — watching every process, every login and every file on your endpoints, and acting the instant something crosses the line. Currently in active development, ahead of public launch.
Windows Linux macOS Agentic Response

68%

Development Complete

EDR+XDR

Unified In One Agent

7

Autonomous Response Actions

Q2

2026 Public Launch
Martinet — AI-native endpoint security and autonomous XDR platform
STATUS: BUILDING IN THE OPEN

An agent is learning to
defend on its own

Martinet isn't live yet — our AI engineers are still training the detection models that let it act autonomously. Here's exactly where things stand.

martinet@hackerhub8-lab: ~/build
$ ./build_status --verbose
> Core EDR Agent (Win/Linux/macOS) ....... [COMPLETE]
> Telemetry & Event Pipeline .............. [COMPLETE]
> Behavioral Detection Model .............. [TRAINING]
> Agentic Response Engine .................. [IN PROGRESS]
> Closed Beta Program ...................... [PENDING]
> Public Launch ............................ [PENDING]
$
Overall Build Progress 68%
Concept & Research
Complete
Agent Prototype
Complete
AI Detection Training
In Progress
Closed Beta
Upcoming
Public Launch
Upcoming
WHAT IS MARTINET

An endpoint agent that acts, not just alerts

Most EDR tools tell you something is wrong. Martinet is built to fix it — automatically, in seconds, without waiting for a human to be online.

EDR + XDR, UNIFIED

Every endpoint, one correlated view

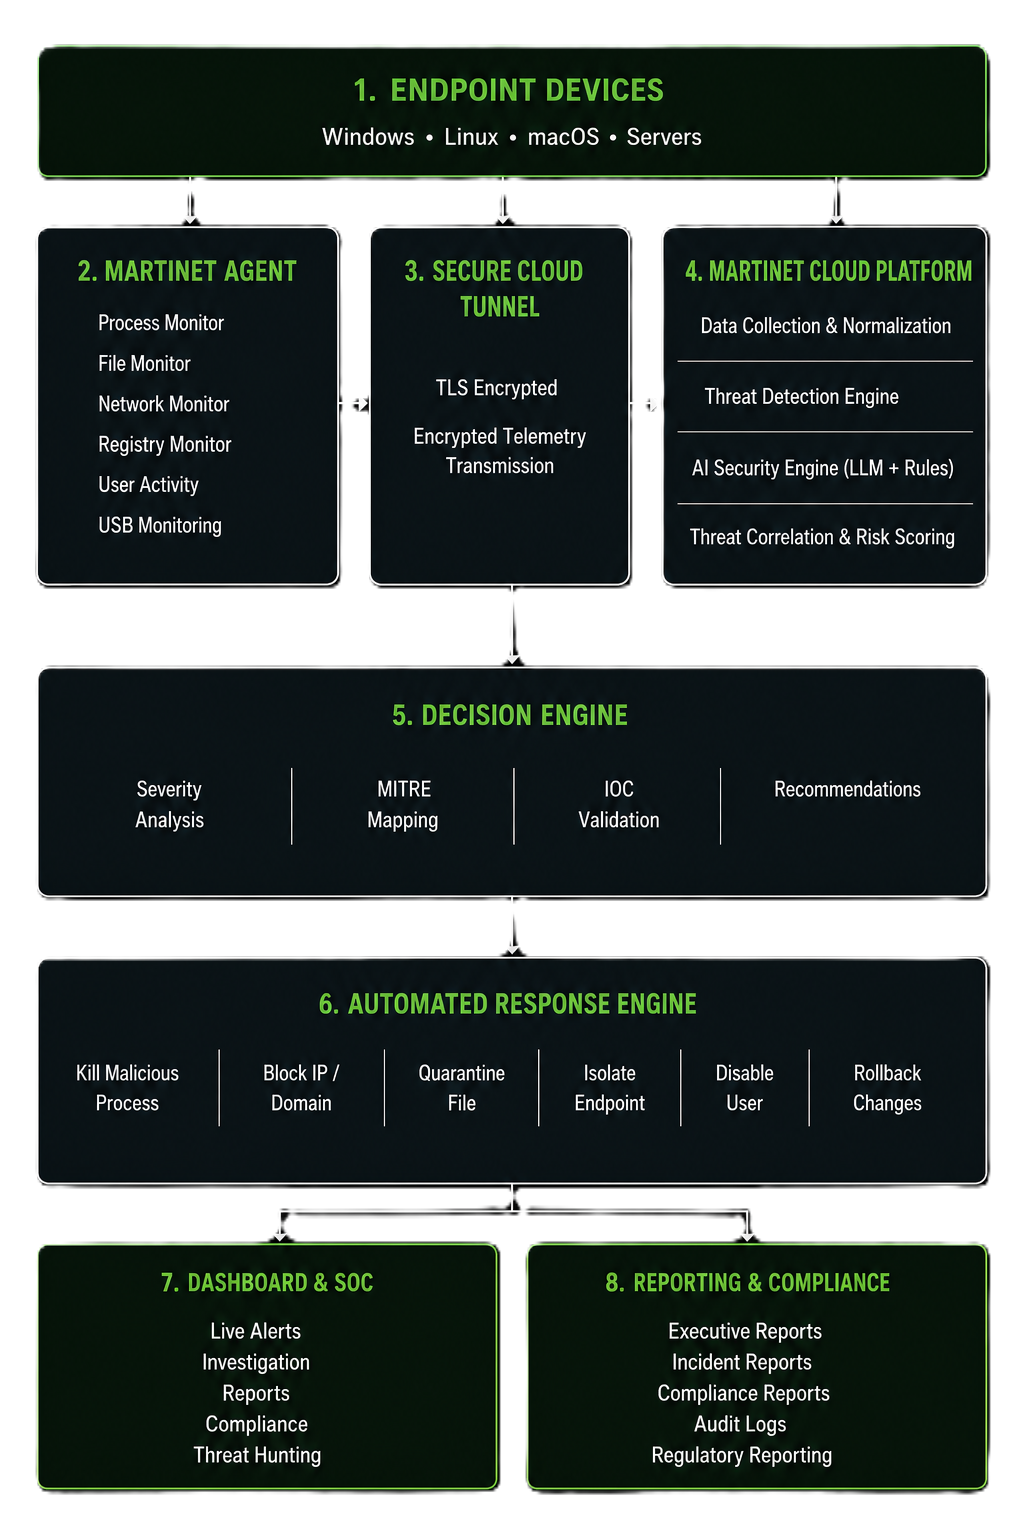
Lightweight agents on Windows, Linux and macOS stream process, file, registry, USB and user-activity telemetry into one platform — correlated across your entire fleet, not siloed per-device.

AGENTIC & AUTONOMOUS

Response happens before you wake up

When Martinet's AI confirms a threat, it doesn't just notify — it kills the process, quarantines the file, isolates the endpoint and opens an incident ticket, automatically, before damage spreads.

WHO IT'S FOR

Built for every team with endpoints to protect

From a lean startup fleet to thousands of enterprise devices, one agent scales across all of them.

SMEs

Enterprise-grade endpoint protection without a large security team.

Startups

Scalable security infrastructure that grows with your headcount.

Enterprises

Centralized visibility and control across large endpoint fleets.

Educational Institutions

Universities, colleges, training centers and research bodies.

Healthcare

Hospitals, clinics, laboratories and healthcare providers.

Financial Institutions

Banks, fintechs, NBFCs and payment service providers.

Government

Public sector agencies needing endpoint monitoring and compliance.

MSSPs

Security providers managing multiple customer environments.

HOW IT WORKS

From telemetry to autonomous response

Three steps, running continuously, on every endpoint you deploy it to.

01

Deploy Lightweight Agents

A single lightweight agent installs on Windows, Linux or macOS and starts streaming process, file, registry, USB and user-activity telemetry in real time — no heavy footprint, no performance hit.

02

AI Detects & Correlates

Behavioral analytics, machine learning and threat intelligence fuse signals across every endpoint — surfacing attack chains a single device's logs would never reveal on their own.

03

Autonomous Response Executes

Confirmed threats trigger action immediately — kill the process, quarantine the file, isolate the endpoint, block the IP — while an incident ticket is created for your team automatically.

CORE CAPABILITIES

Everything a modern SOC needs, in one agent

Nine disciplines working together instead of nine disconnected tools.

Endpoint Detection & Response

Continuous visibility into everything happening on the device.

  • Process & application monitoring
  • Registry & file integrity monitoring
  • USB device monitoring
  • Endpoint risk scoring

Extended Detection & Response

Connecting the dots across your entire endpoint fleet.

  • Multi-source threat correlation
  • Cross-endpoint threat analysis
  • Security event aggregation
  • Attack chain visibility

AI Security Agent

A copilot that investigates alongside your team.

  • AI-powered threat investigation
  • Natural language security queries
  • Threat summarization
  • Automated recommendations

Agentic Response Actions

Real containment, executed without waiting for a human.

  • Kill malicious processes
  • Quarantine infected files
  • Isolate compromised endpoints
  • Auto-create incident tickets

Vulnerability Management

Knowing what's exposed, before it's exploited.

  • Vulnerability scanning
  • CVE monitoring
  • Risk-based prioritization
  • Remediation tracking

Threat Intelligence

Global threat data, applied to every endpoint instantly.

  • Threat intelligence feeds
  • IOC matching
  • Threat enrichment
  • Threat hunting support

Security Analytics

Understanding your posture at a glance, org-wide.

  • Security posture scoring
  • Department-wise scoring
  • Threat trend analysis
  • Employee activity analytics

Compliance Management

Audit-ready evidence baked into daily operations.

  • ISO 27001 & SOC 2
  • GDPR & HIPAA
  • PCI DSS
  • Continuous compliance reporting

SIEM & Security Operations

The operational backbone for your SOC team.

  • Log ingestion & event correlation
  • Incident management
  • Security dashboards
  • Security reporting
PATCH MANAGEMENT HARDWARE & SOFTWARE ASSET INVENTORY LIFECYCLE TRACKING FORCE PASSWORD RESET BLOCK MALICIOUS IPs
AGENTIC IN ACTION

What autonomous response looks like

A preview of how Martinet's response engine will act on your endpoints — detect, decide, and neutralize, in seconds.

LIVE RESPONSE FEED — PREVIEW
Malicious process detected on FIN-LAPTOP-14
Behavioral match: credential-dumping pattern · 00:00:01
PROCESS KILLED
Suspicious payload written to disk
SHA-256 matched known ransomware family · 00:00:02
FILE QUARANTINED
Outbound connection to known malicious IP
Threat intel match: C2 infrastructure · 00:00:02
IP BLOCKED
Lateral movement risk on affected endpoint
Endpoint removed from network segment · 00:00:03
ENDPOINT ISOLATED
Incident ticket auto-generated for SOC review
Full timeline & evidence attached · 00:00:04
TICKET CREATED
SNEAK PEEK

An early look at the console

Design in progress — subject to change before launch.
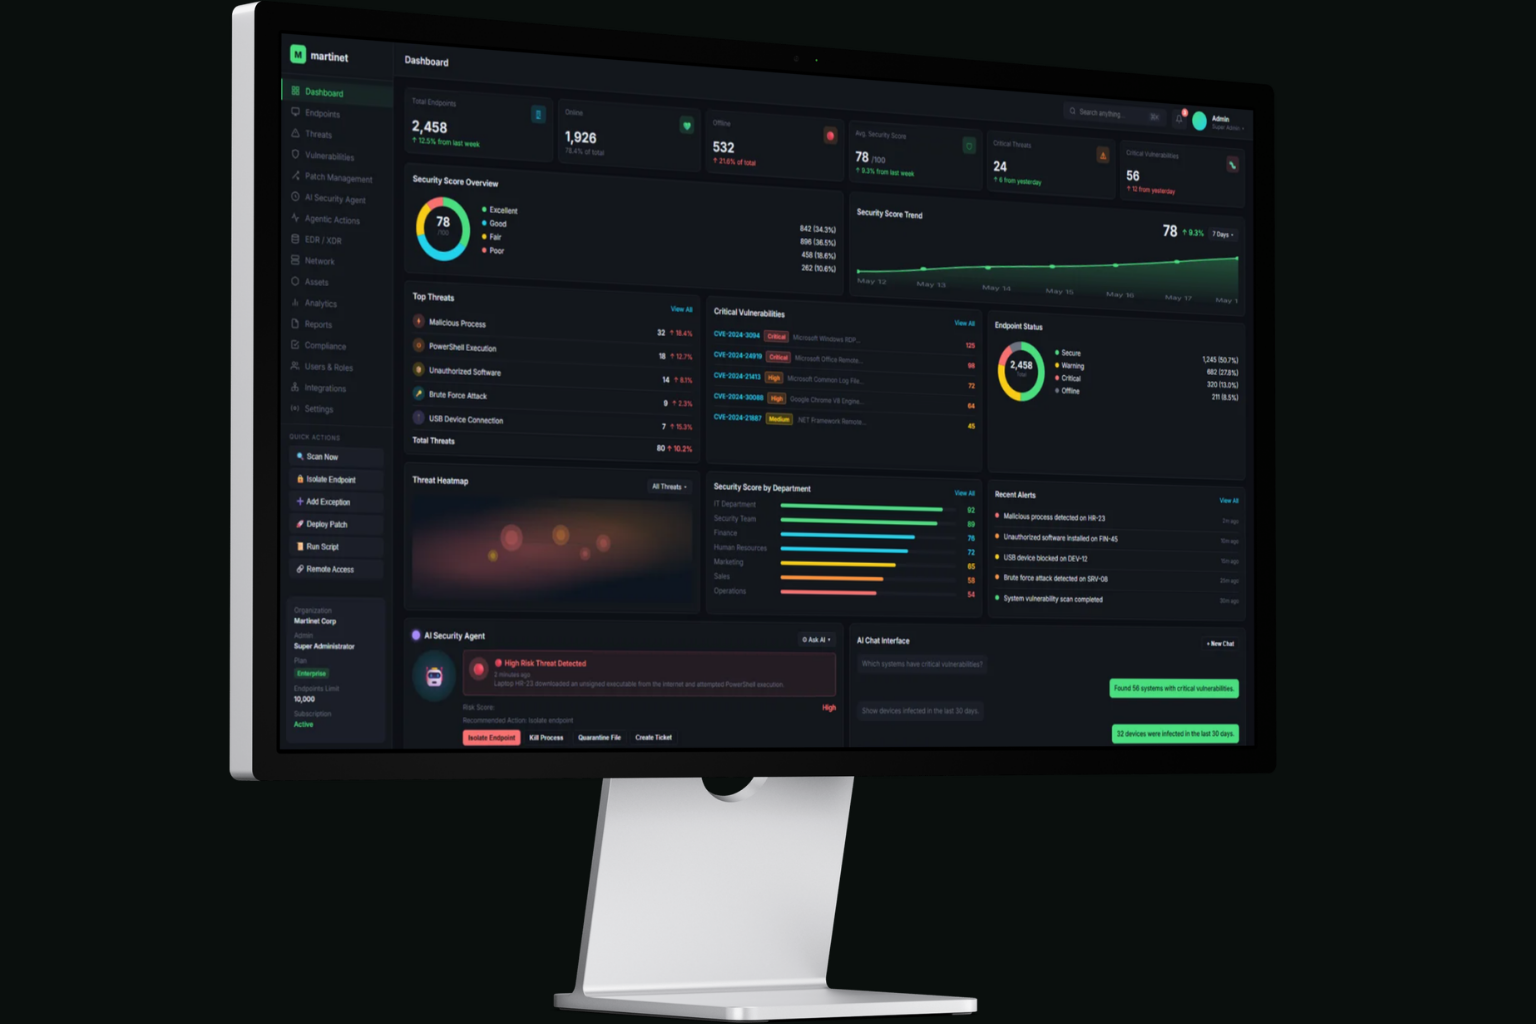
martinet.hackerhub8.com/dashboard
Martinet security dashboard — early concept preview
WHY MARTINET

Not another EDR agent. A drillmaster.

Traditional EDR watches and alerts. Martinet watches, decides, and acts.

Traditional EDR

  • Alerts you, waits for a human to act
  • Separate tool for vulnerability management
  • Separate tool for compliance reporting
  • Per-endpoint view, no cross-correlation
  • Manual incident ticket creation
  • Response measured in hours

Martinet

  • Detects and responds autonomously
  • Built-in vulnerability management
  • Built-in compliance monitoring
  • XDR correlation across the whole fleet
  • Incident tickets created automatically
  • Response measured in seconds
WHO'S BUILDING MARTINET

Engineered by HackerHub8

An Indian cybersecurity startup building next-generation, AI-driven security — by specialists across every layer of the stack.

Endpoint Security Threat Detection & Response Vulnerability Management Artificial Intelligence Security Operations (SOC) Cloud Security Compliance & Governance
PLANS & PRICING

Expected launch pricing

Priced per endpoint, per month. Martinet is still in development — pricing below reflects our current plan and may change before public launch. Early access members get it locked in first.

STARTER PLAN
₹99 / endpoint / mo
Recommended for 10 – 50 endpoints
  • Endpoint Monitoring
  • EDR Protection
  • Threat Detection
  • Security Dashboard
  • Basic Reporting
JOIN EARLY ACCESS
ENTERPRISE PLAN
₹399 / endpoint / mo
Recommended for 500+ endpoints
  • Everything in Professional
  • XDR Capabilities
  • Agentic Response Actions
  • SIEM Integration
  • Custom Compliance Reports
  • Dedicated Support & Advanced Threat Hunting
JOIN EARLY ACCESS

Be first through the door

Join the early access list and get priority onboarding, founder pricing and a direct line to our engineering team when Martinet opens for beta.

MSSP / MULTI-TENANT PLAN — CUSTOM PRICING · Multi-tenant management, customer segmentation, white label options, centralized SOC dashboard, bulk endpoint management. Talk to us →

COMING SOON

Be there when the
agent goes live

Martinet is in active development. Join the early access list to get founder pricing, priority onboarding and updates straight from our engineering team.

Average response within 30 minutes