Regulations change fast, and non-compliance costs more than the fix ever would. Our GRC practice manages your entire compliance journey — governance, risk and regulatory obligations — so your business stays audit-ready, always.
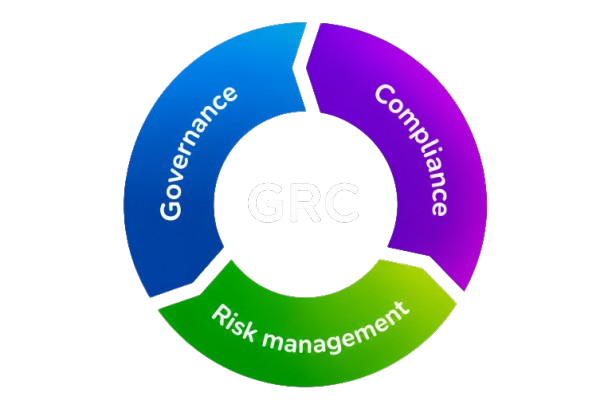
Three disciplines, one connected system. We manage the policies, the risk register and the regulatory obligations so your leadership always has a clear, defensible picture.
We design and maintain the security policies, roles and accountability structures that keep your organization aligned — documented, communicated and enforced.
We identify, score and track business risk continuously, so decisions are made with real visibility instead of assumptions.
From ISO 27001 to DPDP, we map your obligations, close the gaps and keep the evidence ready long before an auditor ever asks for it.
Non-compliance isn't just a fine — it's lost deals, lost trust and lost time. GRC turns regulation from a threat into a competitive advantage.
Stay ahead of DPDP, GDPR, RBI and sector-specific mandates before non-compliance becomes a fine.
Certifications and audit-ready evidence are often the deciding factor in enterprise and government contracts.
A live risk register means leadership makes decisions with facts, not guesswork, at every stage of growth.
Demonstrable governance signals to customers and partners that their data is genuinely safe with you.
From first advisory call to continuous audit readiness — one team, one roadmap.
Strategic guidance to build a compliance roadmap suited to your business and sector.
Ongoing management of your obligations, policies and evidence.
Internal and external audit readiness, run the way real auditors expect.
Practical data protection controls that satisfy both regulators and customers.
A living register of business and cyber risk, scored and tracked.
Making compliance a habit, not a once-a-year scramble.
A structured path from assessment to continuous compliance.
Understand your business, sector and existing controls.
Map current posture against the frameworks that apply to you.
Prioritized plan to close gaps, with clear ownership and timelines.
Policies, controls and evidence built and rolled out with your team.
We stand beside you through internal and external audits.
Ongoing monitoring so you're always audit-ready, not just once a year.
Whatever your industry demands, we've mapped it — and kept the evidence ready.
Every GRC engagement can be integrated with Cyber Law AI — our AI legal assistant built specifically for cybersecurity and data protection law.
Cyber Law AI understands cyber regulations, data protection laws and compliance frameworks — so your team gets accurate, current legal guidance without waiting days for a consultant to respond.
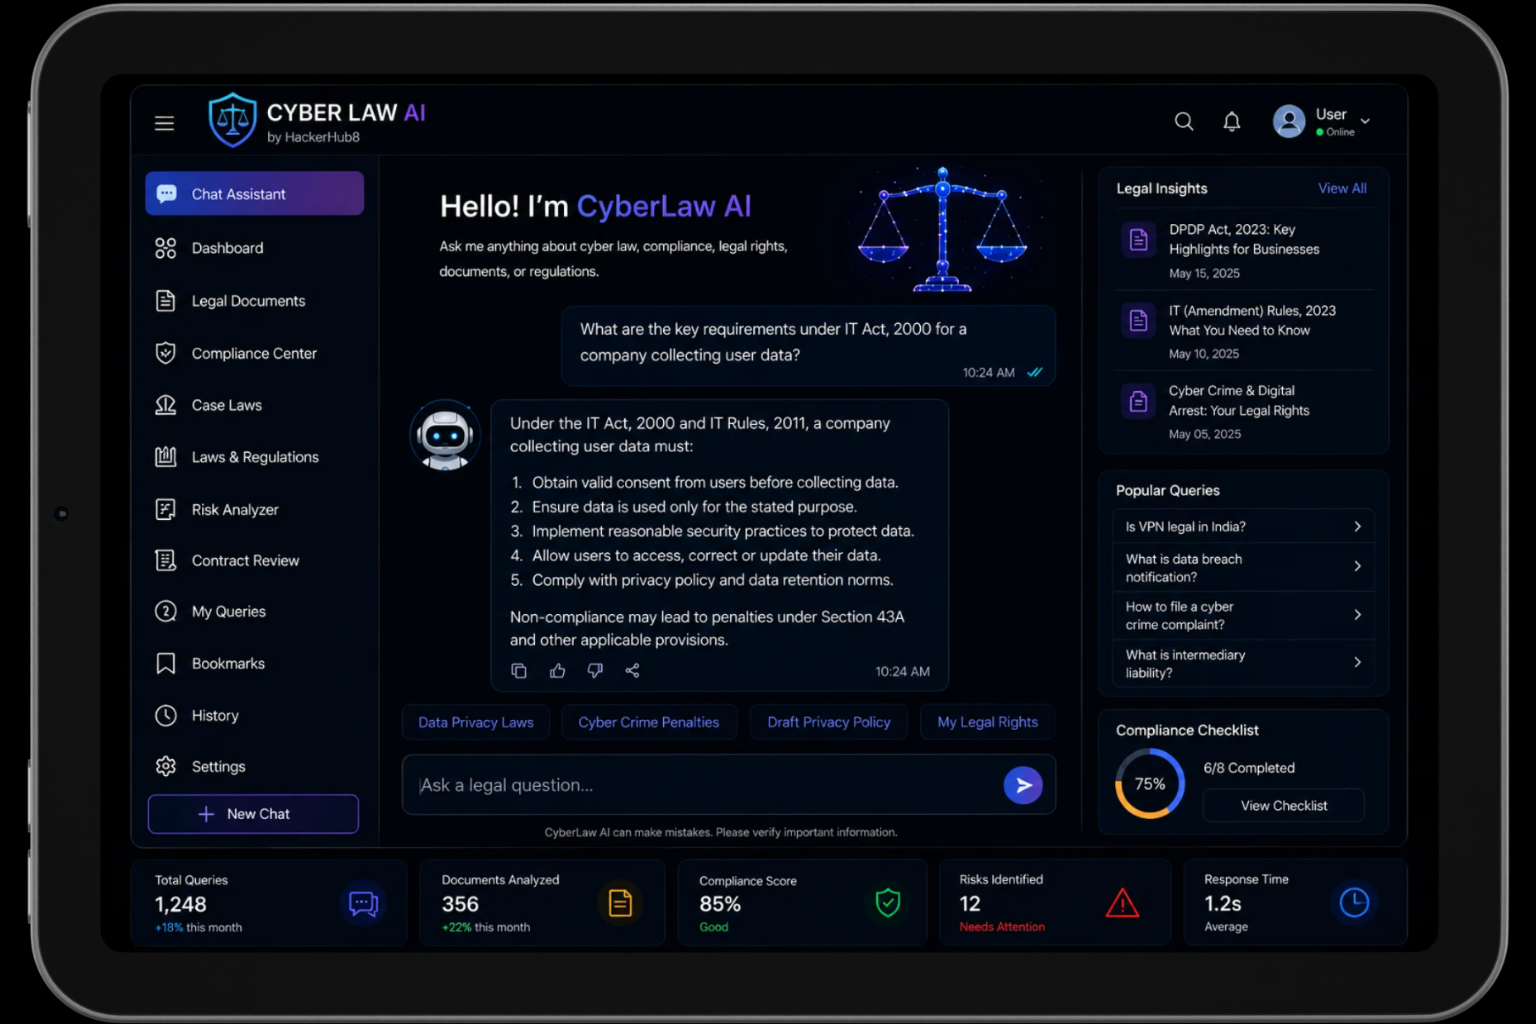
Talk to a GRC advisor about your compliance roadmap, and see Cyber Law AI in action — one call, both covered.
Average response within 30 minutes